root-me.org
Network Ch1 FTP - Authentication
The original challenge can be found at: https://www.root-me.org/en/Challenges/Network/FTP-authentication
This is an easy one: We get a pcap file, which we can open in Wireshark.
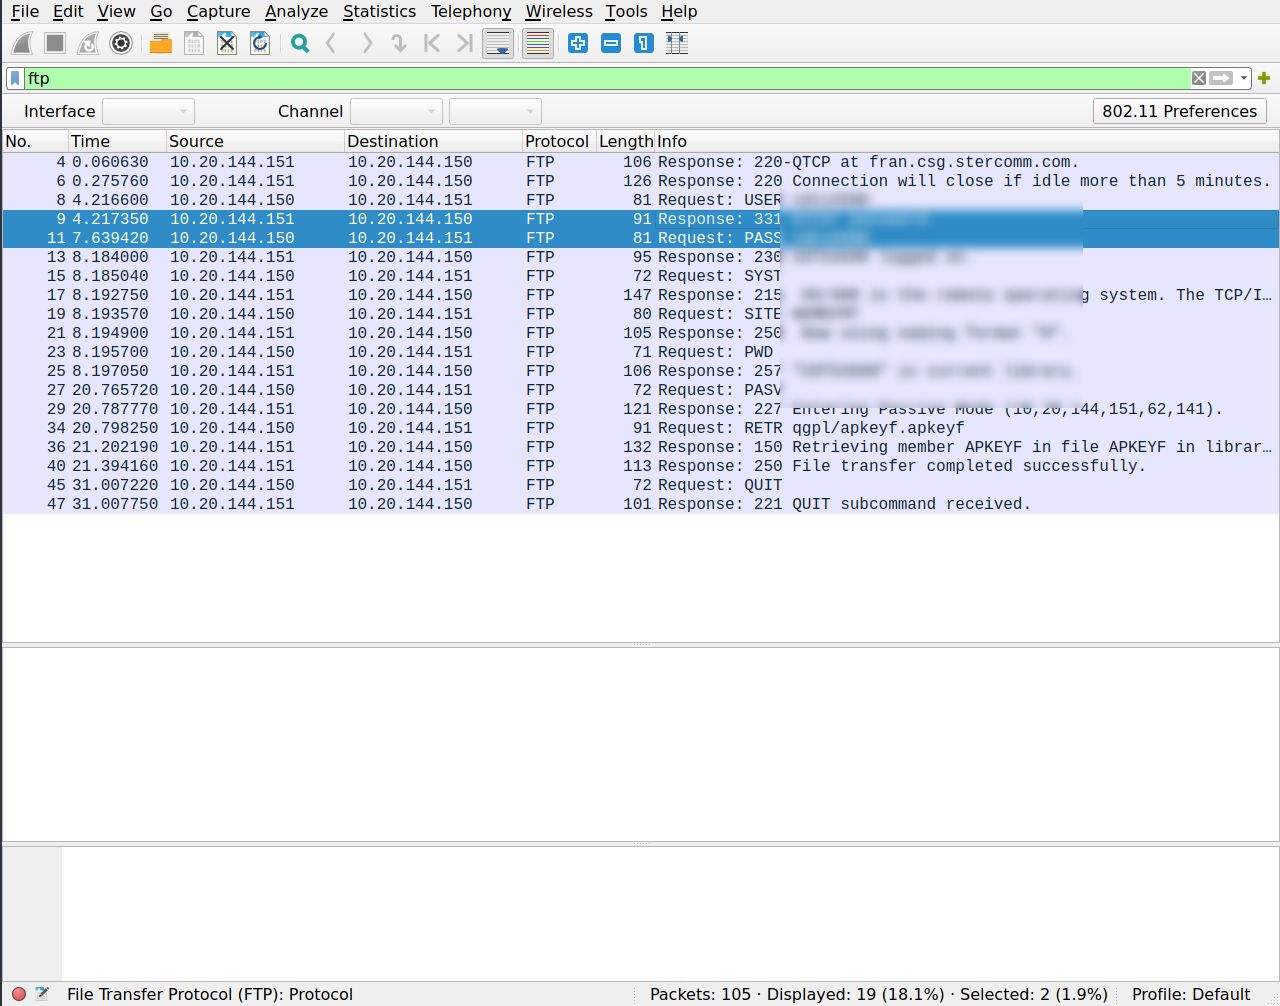 First, filter for the FTP protocol to reduce the output. Second, watch out for requests and responses that say something about login and password. And there you go, boom! Right there is the password. Piece of cake!
Network Ch2 - TELNET - Authentication
The original challenge can be found at: https://www.root-me.org/en/Challenges/Network/TELNET-authentication
This challenge is about telnet, a veteran among network protocols. It has no security features of its own, even though you can often upgrade to encryption via STARTTLS.
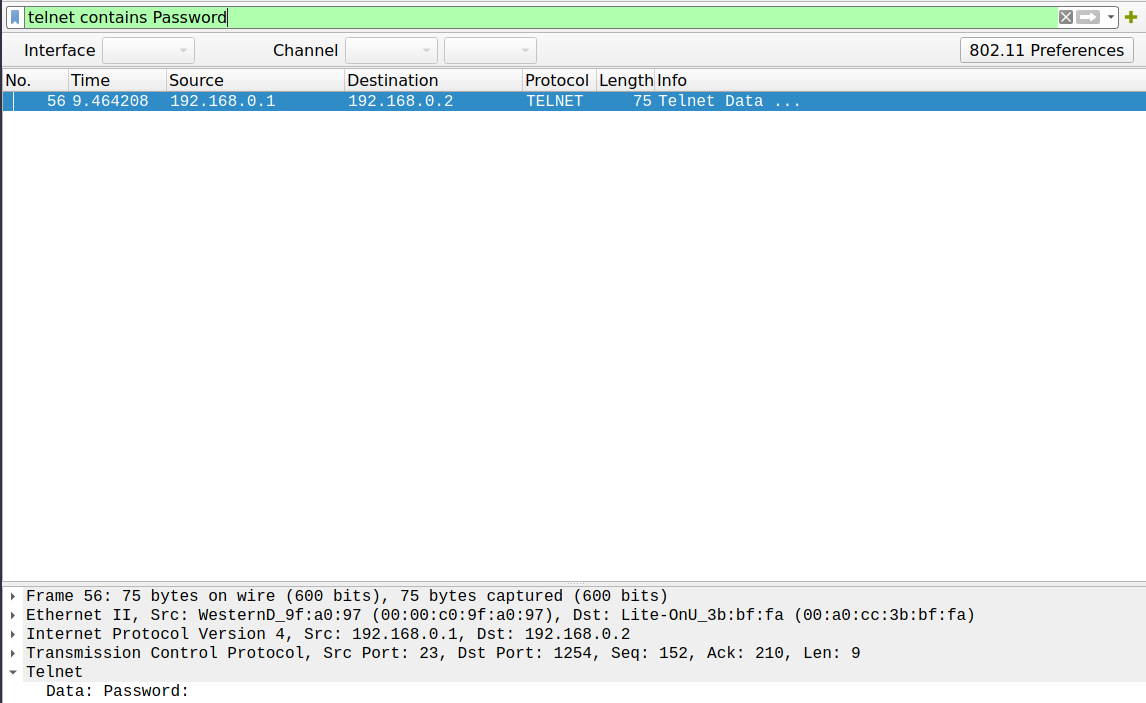
However: We are supposed to uncover a username and password. So just filter for telnet, and it contains the password:
telnet contains Password
Ah, packet 59, there it is, and the following packets contain the cleartext password. Each packet has just a single character. But no worries, it is a pretty short password. After that, telnet contains just some shell commands and can be ignored.
Network Ch3 - Raw Ethernet Frame
The original challenge can be found at: https://www.root-me.org/en/Challenges/Network/ETHERNET-frame
This challenge just gives you a raw hex dump of an Ethernet frame. Inside the frame, the flag has to be found. The following represents the hex dump as supplied by the challenge.
00 05 73 a0 00 00 e0 69 95 d8 5a 13 86 dd 60 00
00 00 00 9b 06 40 26 07 53 00 00 60 2a bc 00 00
00 00 ba de c0 de 20 01 41 d0 00 02 42 33 00 00
00 00 00 00 00 04 96 74 00 50 bc ea 7d b8 00 c1
d7 03 80 18 00 e1 cf a0 00 00 01 01 08 0a 09 3e
69 b9 17 a1 7e d3 47 45 54 20 2f 20 48 54 54 50
2f 31 2e 31 0d 0a 41 75 74 68 6f 72 69 7a 61 74
69 6f 6e 3a 20 42 61 73 69 63 20 59 32 39 75 5a
6d 6b 36 5a 47 56 75 64 47 6c 68 62 41 3d 3d 0d
0a 55 73 65 72 2d 41 67 65 6e 74 3a 20 49 6e 73
61 6e 65 42 72 6f 77 73 65 72 0d 0a 48 6f 73 74
3a 20 77 77 77 2e 6d 79 69 70 76 36 2e 6f 72 67
0d 0a 41 63 63 65 70 74 3a 20 2a 2f 2a 0d 0a 0d
0a
There are several options. The fastest: Just decode the whole hex dump to a string. The last few bytes will get you nearly to the answer. But I suggest a deeper dive, so let's dissect the dump!
Hint: I know Ethernet has a preamble field, but it is not part of the packet. The packet starts right with the destination and source addresses.
We have 14 lines: the first 13 with 16 bytes each, and the last line with only one entry. We can transfer them to a .pcap file or just work on the raw information from the dump.
If we analyse the frame, we see that the first 14 bytes are exactly the size of an Ethernet frame header, therefore this should be the header. Having a deeper look at:
00 05 73 A0 00 00
tells us that this is the destination address. As this is on the link layer, we are talking about MAC addresses. Thus, the MAC address is 00:05:73:a0:00:00. The first three hex values are the vendor-specific part, \(00 05 73\), which tells us it is a Cisco device.
E0 69 95 D8 5A 13 86 DD
The above encodes the source address. Like the destination address, it is a MAC address, which tells us it is from Pegatron Corporation (vendor part E06995).
The next two bytes are the type field, which declares the protocol run on the network layer. Thus, \(86 DD\) tells us it is an IPv6 packet! (Well, they are bleeding-edge guys at root-me ^^)
As the IPv6 header is 40 bytes long, it starts at byte 14 (counting from 0). The payload is 155 bytes, containing a TCP packet on the transport layer. Some features that can be extracted are the hops (TTL in IPv4, length of 8 bits = 0-255), which are set to \(64 = 2^6\). They encoded a nice source address: \(2607:5300:60:2abc::bade:c0de\).
Next is the transport layer with the TCP packet. The header tells us the source port is hex \(96 74\) or \(38516\) (outgoing ports are random ephemeral ports), and as the number is below the IANA-suggested range of 49152 to 65535, it can be assumed that this is a Linux (\(32768\) to \(60999\)) or FreeBSD (\(10000\) to \(65535\) as ephemeral ports) system.
The destination port is 80 (hex 00 50), the standard web port. This makes sense, as otherwise we would have to handle TLS crypto stuff for HTTPS. It also tells us what is waiting on the application layer: HTTP. The next two bytes (hex 80 18) hold the header length of 32 bytes and the flags: only PSH and ACK are set, all other flags are 0. We skip the rest of the TCP stuff - if you are interested, go ahead and analyse it.
Okay: This is the final part you have been waiting for -- HTTP
47  45  54  20  2F  20  48  54  54  50
2F  31  2E  31  0D  0A  41  75  74  68  6F  72  69  7A  61  74
69  6F  6E  3A  20  42  61  73  69  63  20  59  32  39  75  5A
6D  6B  36  5A  47  56  75  64  47  6C  68  62  41  3D  3D  0D
0A  55  73  65  72  2D  41  67  65  6E  74  3A  20  49  6E  73
61  6E  65  42  72  6F  77  73  65  72  0D  0A  48  6F  73  74
3A  20  77  77  77  2E  6D  79  69  70  76  36  2E  6F  72  67
0D  0A  41  63  63  65  70  74  3A  20  2A  2F  2A  0D  0A  0D
0A
This is the HTTP part of the message: an HTTP GET request. The first 3 bytes are the GET method, followed by one byte for the URI (2f), then the request version HTTP/1.1.
Finally, we have HTTP basic authorization:
41  75  74  68  6F  72  69  7A  61  74
69  6F  6E  3A  20  42  61  73  69  63  20  59  32  39  75  5A
6D  6B  36  5A  47  56  75  64  47  6C  68  62  41  3D  3D  0D
0A
We can decode this to the ASCII string Authorization: Basic HEREISSOMETHING==\r\n. The two equal signs tell us that this is base64 encoded. Via shell you can decode this:
base64 -d FILENAME
#or
echo "BASECODE==" | base64 -d
So now we have our flag and can get the points. Really nice challenge for beginners interested in networking, as you analyse crucial parts of the ISO/OSI model. It was fun to dig through this.
Network Ch4 Twitter Authentication
The original challenge can be found at: https://www.root-me.org/en/Challenges/Network/Twitter-authentication-101
We have to retrieve the password for a Twitter session. As Twitter sits on the application layer and we got a pcap file, this should be pretty easy.
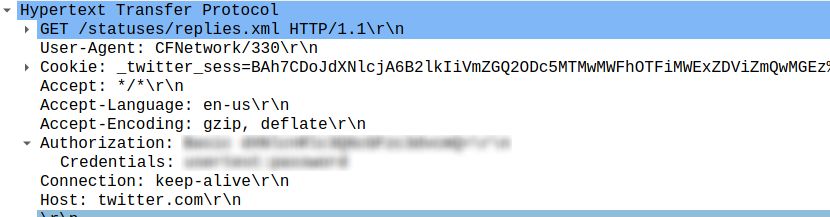
After opening the pcap file, we see it's HTTP in the application layer. If we investigate further, we find the http.authorization section with a basic authentication mechanism. This means no real security, as the password is only encoded via Base64. Wireshark also shows it in clear text in the authorization section, where it states the credentials.
Network Ch5 Bluetooth - Unknown file
The original challenge can be found at: https://www.root-me.org/en/Challenges/Network/Bluetooth-Unknown-file
The goal of this challenge is to find out the MAC address and device name, then calculate the SHA1 value of this concatenation.
We get a binary file that is a BTSnoop file. If we run the file command, we get:
file ch18.bin
ch18.bin: BTSnoop version 1, HCI UART (H4)
This file can be analysed via Wireshark. Here comes the big advantage of Wireshark: after opening the file, we can simply display the Bluetooth device.
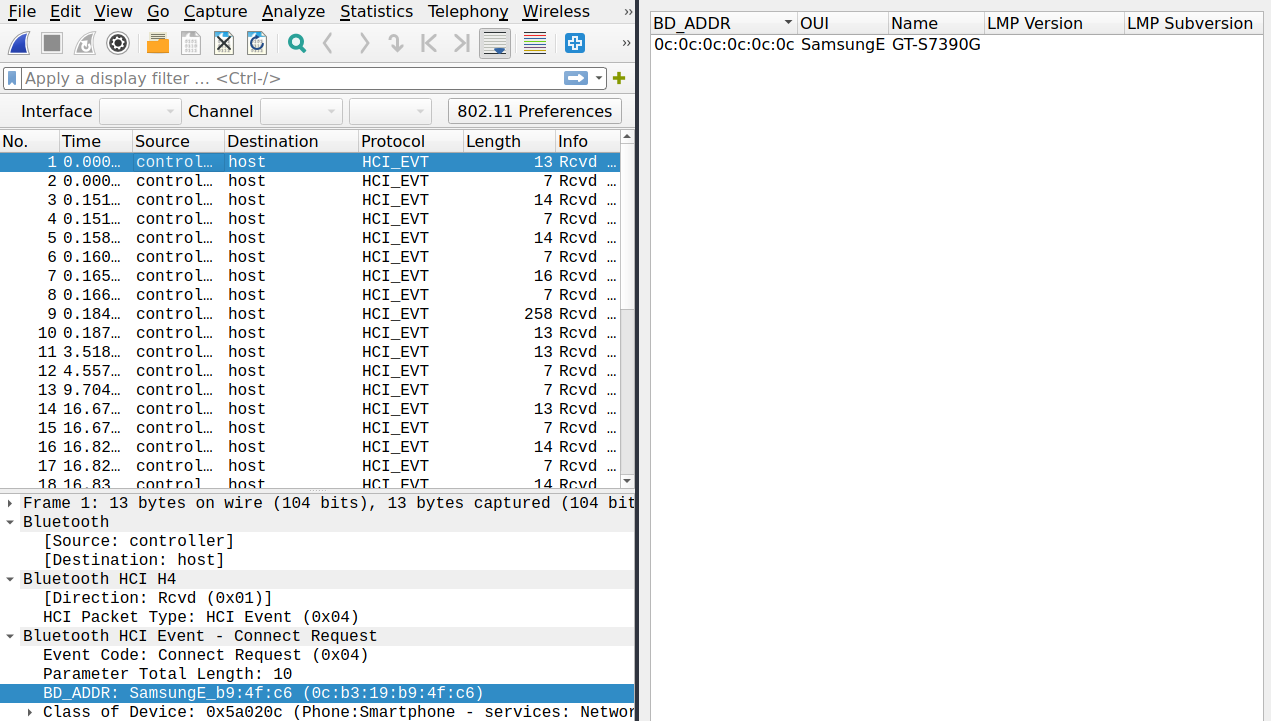
This will get us the device name and the MAC address, which we simply have to concatenate and run SHA1 over.
The MAC address is
0c:b3:19:b9:4f:c6
Device Name:
C6GT-S7390G
And now just put it into the terminal like this:
echo "XXXXXXXXXXXXXXXXXXX" | sha1sum